Web Hosting: How It Actually Works (Step by Step)
By the GuideMyHost Team. We manage our own sites on DreamHost’s shared hosting and reference our own setup where it’s relevant. Last updated August 2026.
How does web hosting work? You already know what web hosting is: a service that stores your website’s files on a server so people can reach it online. This guide goes one level deeper — what actually happens, in order, between someone typing your domain and your page appearing on their screen.
None of this requires a computer science degree to follow. But understanding the sequence helps you troubleshoot a slow site, understand what a CDN or SSL certificate is actually doing, and ask your host smarter questions when something breaks.
How Web Hosting Works: The Short Version
If you only remember one line, remember this sequence:
Browser → Cache check → DNS lookup → Server connection → Security handshake → HTTP request → Server processing → Response → Render
Every one of those steps takes time — usually milliseconds, but they add up, and any one of them can be the reason a site feels slow. Let’s walk through each one.
Step 1: The Browser Checks What It Already Knows
Before your browser asks the internet anything, it checks itself.
- Browser cache: has this domain been visited recently? If so, some information (including the DNS result) may already be stored.
- OS-level cache: your operating system keeps its own short-term memory of recent domain lookups.
- Hosts file: a local file that can manually map a domain to an IP address, bypassing DNS entirely (rarely used outside of development/testing).
If nothing useful is cached, the browser moves on to asking the internet where your site actually lives.
Step 2: DNS Resolution — Finding the Right Server
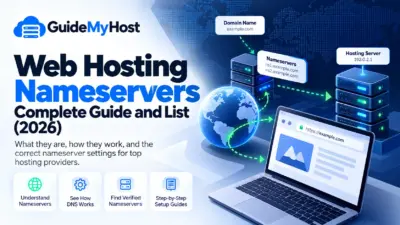
This is the step most people have heard of but few actually understand. DNS (Domain Name System) exists because computers route traffic using numeric IP addresses, not names like example.com — so something has to translate one into the other.
Here’s the actual chain of requests, in order:
- Your device asks a recursive resolver (often run by your ISP, or a public one like Google’s
8.8.8.8or Cloudflare’s1.1.1.1) to resolve the domain. - The recursive resolver checks its own cache. If it has already resolved this domain recently, it returns the answer immediately — no further steps needed.
- If not cached, it asks a root server which top-level domain (TLD) server handles
.com(or.org,.io, etc.). - The root server points it to the correct TLD server — it doesn’t know your site’s address, just who to ask next.
- The recursive resolver asks the TLD server about your specific domain, and receives the address of your domain’s authoritative name server — usually run by your hosting provider or DNS service.
- The recursive resolver queries that authoritative server directly, which finally returns the actual IP address tied to your domain.
- The IP address is cached (for a duration set by your DNS records’ TTL — “time to live”) and handed back to your browser.
That’s four to seven round trips happening in the background, usually completing in well under a second — often just tens of milliseconds if results are cached anywhere along the chain. For a deeper technical breakdown of this exact process, see Cloudflare’s guide to DNS resolution.
Step 3: The Browser Connects to the Server
With an IP address in hand, the browser opens a TCP connection to your hosting server — a three-step handshake (SYN, SYN-ACK, ACK) that establishes a reliable channel before any actual website data is exchanged. This happens whether your site uses HTTP or HTTPS.
Step 4: The Security Handshake (HTTPS/TLS)
If your site uses HTTPS — and the overwhelming majority of sites now do — the browser and server perform a TLS handshake before any content is transferred:
- The server presents its SSL/TLS certificate, proving it’s actually who it claims to be.
- The browser verifies that certificate against trusted certificate authorities.
- Both sides agree on an encryption method and exchange keys.
- From this point forward, everything sent between browser and server is encrypted.
This is why HTTPS matters beyond the padlock icon: without it, anything sent between a visitor and your server — including form submissions, login details, or payment information — could be intercepted in plain text.
Step 5: The Browser Sends the HTTP Request
Now the browser sends an actual HTTP request — asking specifically for the resource it needs, usually starting with your homepage (GET /). This request includes details like the browser type, accepted content formats, and any cookies already associated with your site.
Step 6: The Server Processes the Request
This is where your hosting environment actually does its job, and what happens here depends heavily on your site type:
- Static sites (plain HTML/CSS/JS): the server simply locates the requested file and prepares to send it back — fast, with minimal processing.
- Dynamic sites (WordPress and similar CMS platforms): the server runs server-side code (commonly PHP), often queries a database for content, assembles the page, and then sends it back. This extra work is one reason dynamic sites can be slower than static ones without caching in place.
- Caching layers, where available, can skip most of this by serving a pre-built version of the page instead of rebuilding it from scratch on every request.
In our own experience running WordPress sites on DreamHost’s shared hosting, this is the step where a decent caching setup makes the most noticeable difference — pages that would otherwise hit the database on every load instead get served from a cached copy in a fraction of the time.
Step 7: The Response Travels Back
The server packages up the requested resource — HTML first, typically followed by separate requests for CSS, JavaScript, images, and fonts — and sends each back over the already-established, encrypted connection.
Step 8: The Browser Renders the Page
Finally, the browser:
- Parses the HTML to build the page structure (the DOM).
- Applies CSS for layout and styling.
- Runs JavaScript for interactivity.
- Paints the finished page to the screen.
This entire sequence — from typing a URL to seeing a fully loaded page — typically happens in well under two seconds on a healthy setup, and often in a fraction of that.
Where a CDN Fits Into This
A Content Delivery Network (CDN) doesn’t replace any of the steps above — it shortens the physical distance some of them travel. Instead of every visitor’s request traveling all the way to your origin server, a CDN caches copies of your static content (images, CSS, JS, sometimes full pages) on servers positioned closer to the visitor geographically. This mainly affects Steps 3 and 7 — the connection and the response travel a shorter physical distance, which particularly helps visitors far from your server’s actual location.
Why This All Matters for Site Speed
Each step above adds latency, and slow steps compound:
| Step | Typical time | What slows it down |
|---|---|---|
| DNS resolution | Milliseconds (cached) to ~100ms+ (uncached) | Uncached lookups, slow DNS provider |
| TCP + TLS handshake | Tens of milliseconds | Server distance, certificate issues |
| Server processing | Milliseconds to seconds | No caching, heavy database queries, underpowered hosting |
| Response transfer | Varies by file size | Large uncompressed images/files, no CDN |
| Browser rendering | Milliseconds to seconds | Unoptimized CSS/JS, render-blocking scripts |
This is also why “which host is fastest” isn’t a complete question — a fast server with no caching can still feel slow on a database-heavy site, and a well-optimized site on modest shared hosting can outperform a poorly configured setup on expensive infrastructure.
What Is Web Hosting? 7 Essential Facts Beginners Should Know
FAQ
How long does DNS resolution actually take? If the result is already cached anywhere along the chain (browser, OS, or resolver), it can be near-instant. An uncached lookup that has to walk the full root → TLD → authoritative chain typically completes in well under a second, but it’s still one of the more variable steps in the process.
Does HTTPS make my site slower? The TLS handshake adds a small amount of overhead, but on modern servers and browsers this is negligible — measured in milliseconds — and it happens once per connection, not per file. The security benefit far outweighs this cost.
Why does my WordPress site feel slower than a plain HTML site? Dynamic sites like WordPress do more work per request — running server-side code and often querying a database — before they can respond. A good caching setup narrows or eliminates this gap by serving pre-built pages instead of rebuilding them each time.
Do I need a CDN? Not always. If most of your visitors are geographically close to your hosting server, the benefit is smaller. If you have a global audience, a CDN can meaningfully cut load times by serving cached content from a location nearer to each visitor.
Is this process different for shared, VPS, or dedicated hosting? The sequence of steps is the same regardless of hosting type. What changes is the speed and consistency of Step 6 (server processing) shared hosting splits server resources among multiple sites, while VPS and dedicated hosting reserve resources for yours alone.